Final project
Problem statement, rephrasing & divergence
Analyze and harden the vulnerabilities of a computing system that you want to secure
- What system is worth protecting? From a content point of view, from a ressource point of view?
- Protection has to be proportionnal to the threat (self-defense principle)
- Does it have to be electronic? Can it be humanware?
- Related to FabLab: 3D files? Machines? Networks?
- Be humble: loads of specialists have already implemented defenses
Ikigai: Modest + Useful + Fun
Convergence
After being delayed several times Fab Futures Cyber ended up being at the same time as my holidays with 3 years olds.
Reading kids magazine led me to the postponed interest I have in graphic facilitation/sketch noting influenced by actors such as SuperTilt and its picto dico.
The work of Julia Evans that I discovered after the network class really impressed me. So I decided to produce a final project really inspired by her work: fun, accessible yet technical.
This resonated with my belief that some obscurity happens in cybersecurity due to the praised tech-savvy approach.
## Securing a FabLab
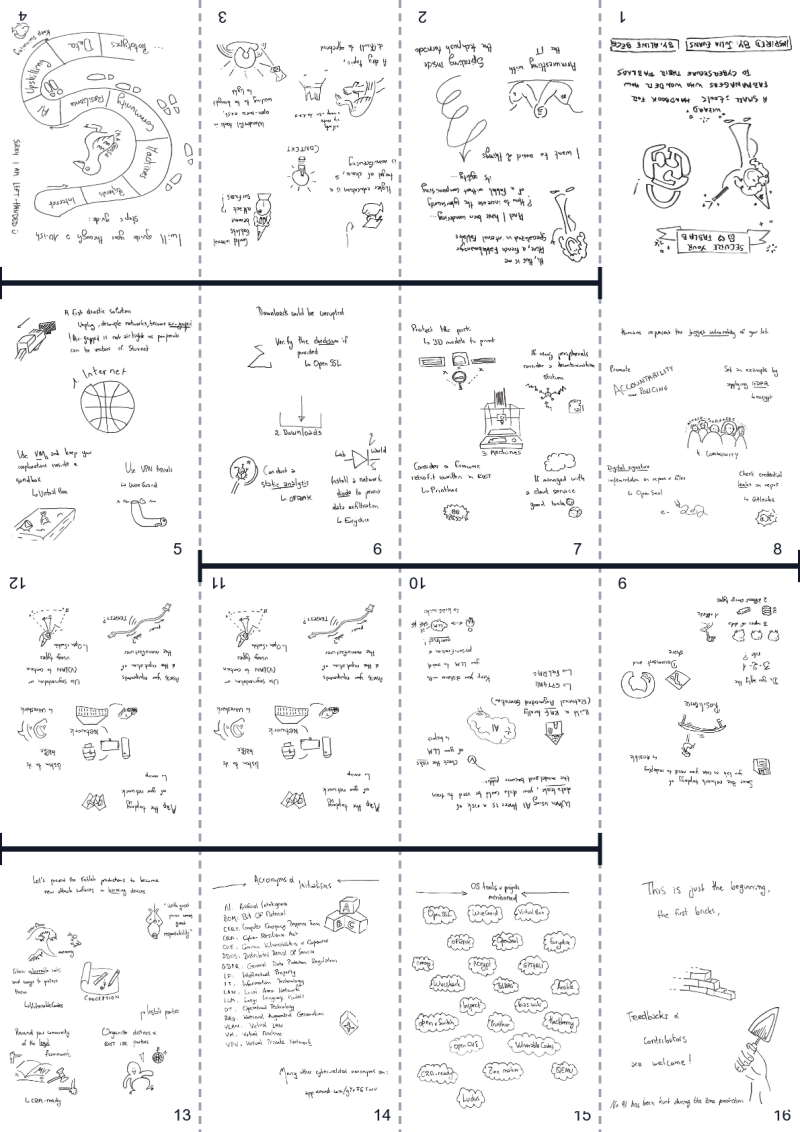
The computing system: The FabLabs The outcome: A zine as an hommage to Wizard zine The hardening: Awareness raised, some tools base examples
10ish steps scenario
A Labmanager wonders on how to protect internal FabLabs.
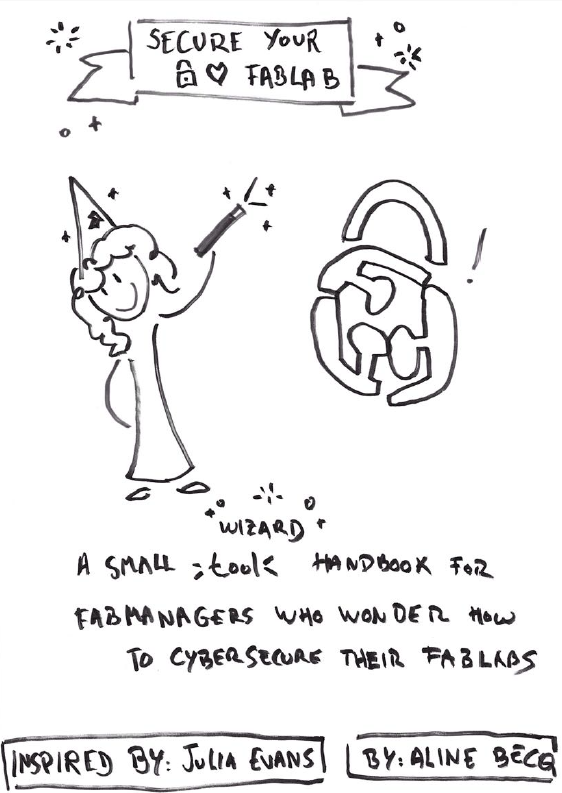
How not to make it a vulnerability for the organization and avoid arm wrestling with the SI?
0. Context
SI aspects are often not taken into consideration at the creation of the Lab. Ideally they should be Secure by Design but the running FabLabs could use some retrofits. FabLabs should be able to test, develop and implement new tools. A need that SI restriction could sometimes hinder. Internal FabLabs could be targets to penetrate the organization network. Even if I never heard of a case.
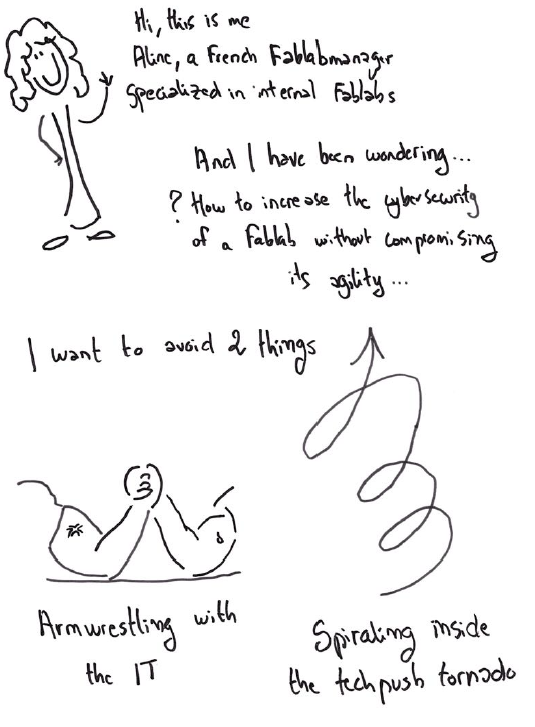
Let’s do a little anticipation, what attacks could a FabLab undergo?
- Ransomware? The data of the FabLab and of its organization are encrypted
- DDOS? The website of the Lab and of its parent entity are not accessible
- OT attack? The machines are damaged
- Cyberespionnage? IP steal? Warez?
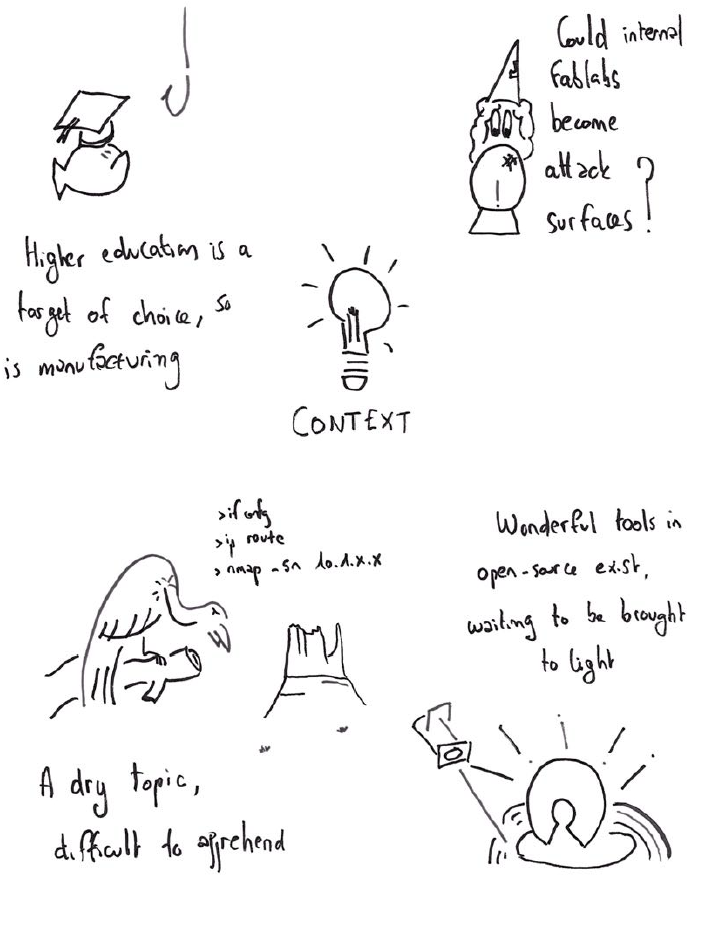
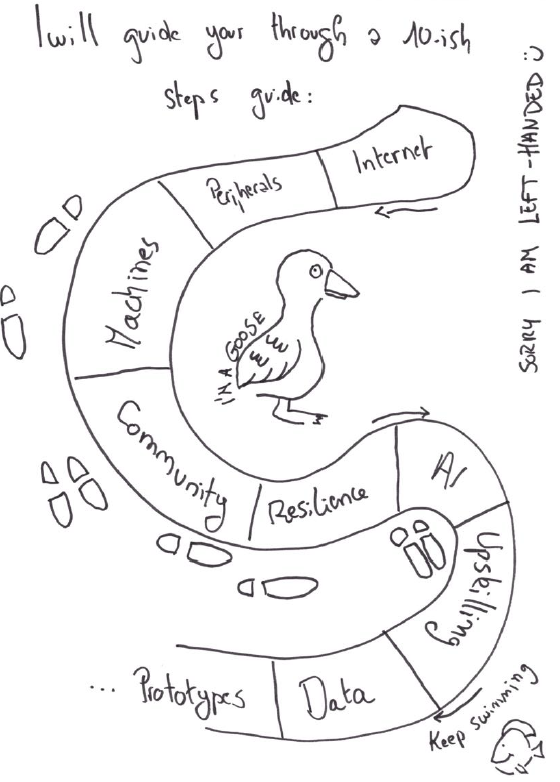
Thanks to the children magazine Abricot I decided to present the summary as a game.
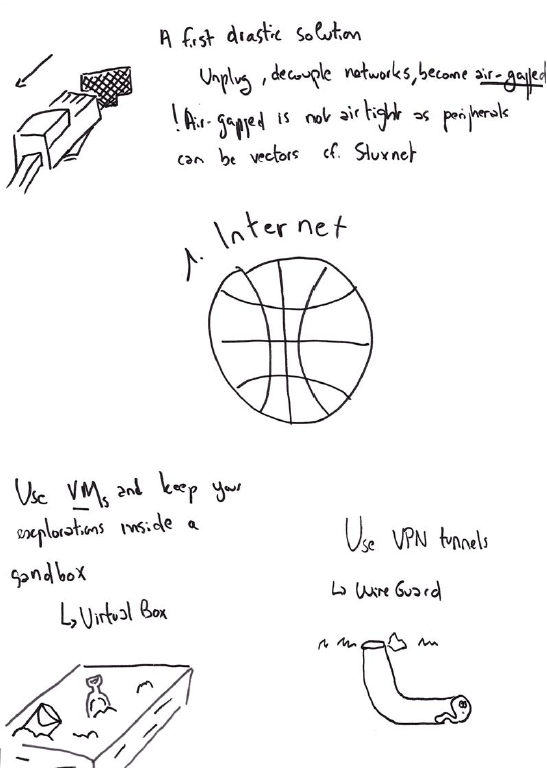
1. Internet
How to safely access Internet?
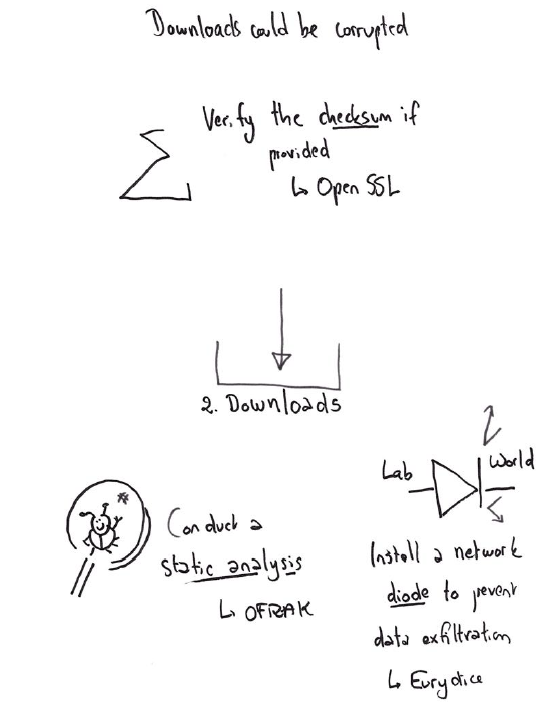
2. Downloads
How to smoothly install and test tools?
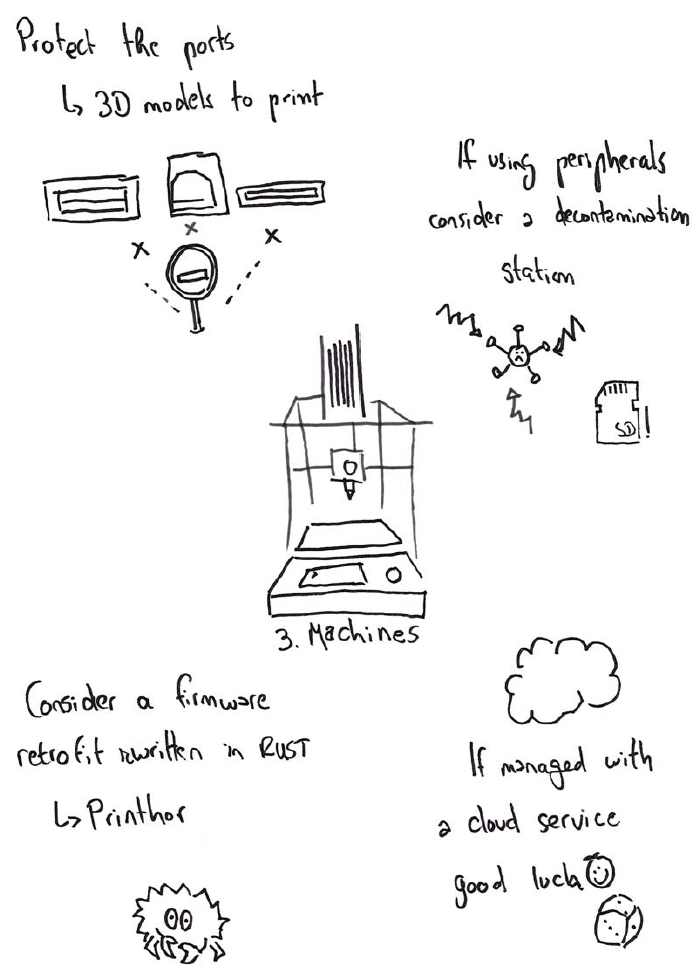
3. Machines
What are the embedded vulnerabilities of your FabLab machines?
Having a worldwide FabLab CERT would be a nice to have
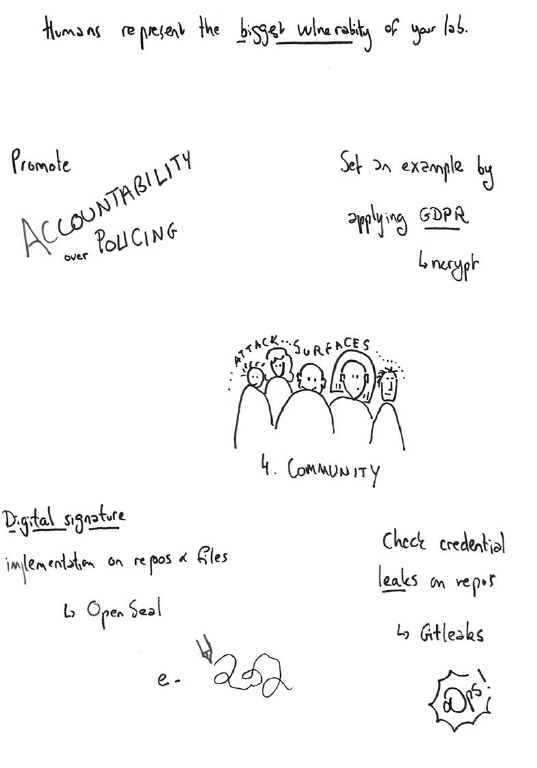
4. Community
*How to promote security without sounding freedom-destroying?
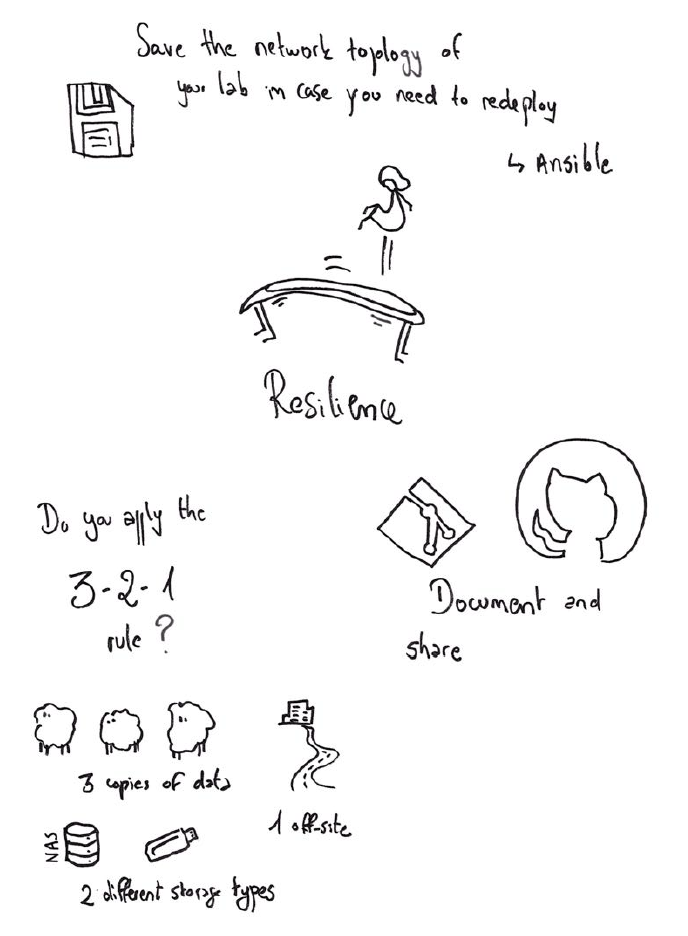
5. Resilience
*If an attack was to happen could we quickly reboot the FabLab?
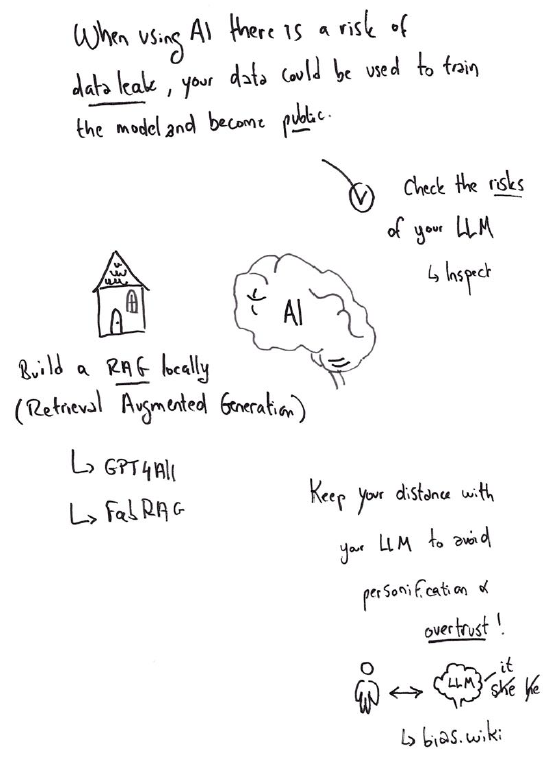
6. AI
*How to benefit from AI power without sending our data into the wild?
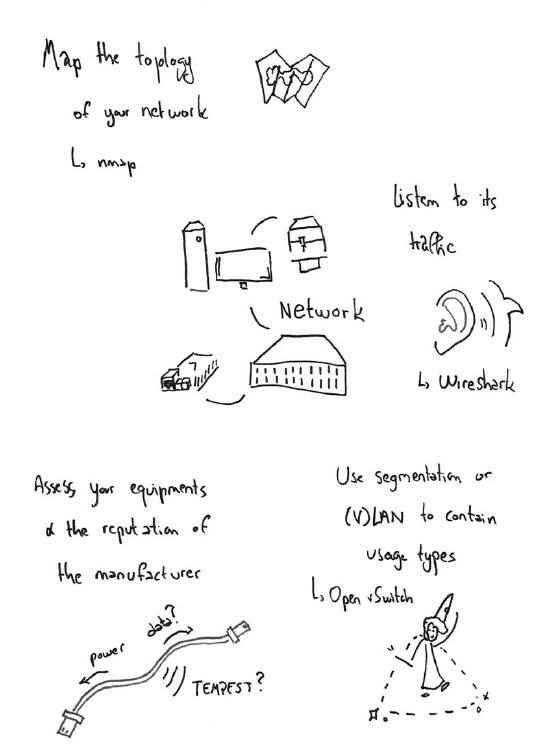
7. Network
*How to own your FabLab network?
8. Equipments
How to explore cyber with your equipements?
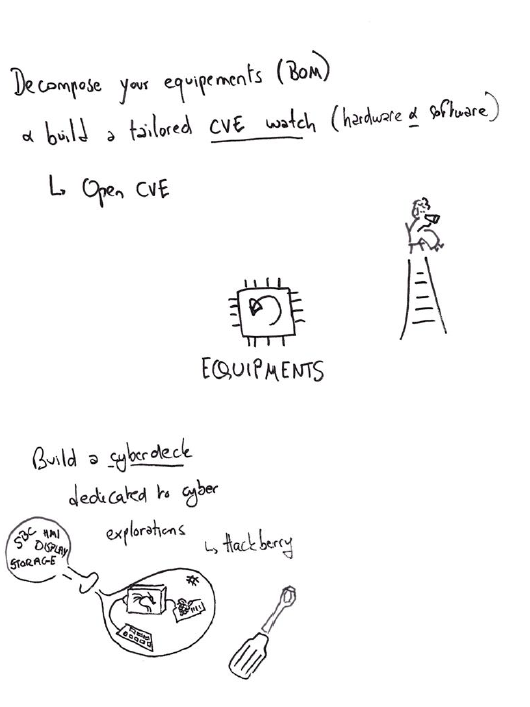
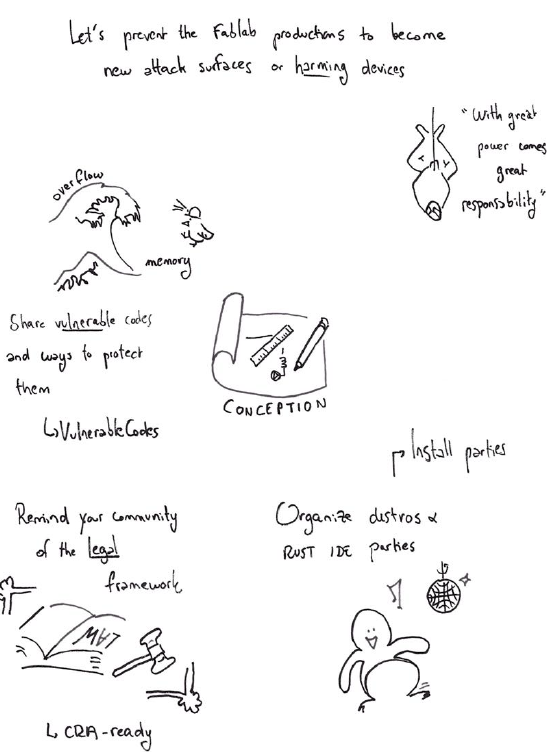
9. Conception
*How to prevent the production of vulnerable or harming hardwares in the FabLab?
10. Data exfiltration/PI How to prevent the data manipulated in the Lab from leaking? Should we?
11. Lexicon Acronyms and initialisms used in the zine explicited.
12. Tools list All tools suggested will be summurized on 1 page as Wizardzine did with Linux network tools.
13. The end Call for contributions
I would love to be able to build a booklet for Fabmanagers on holidays based on this work. In France we have “cahiers de vacances”, more and more adapted to grown-ups.
Also each page should ideally come with 1-2 detailing/explaining pages with precise instructions to favour applications.
An example for OpenCVE
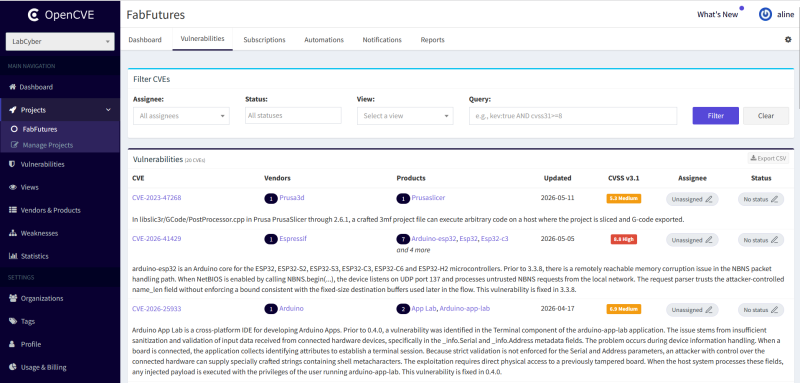
Go to my Zine page to have all pages and the zine to download.