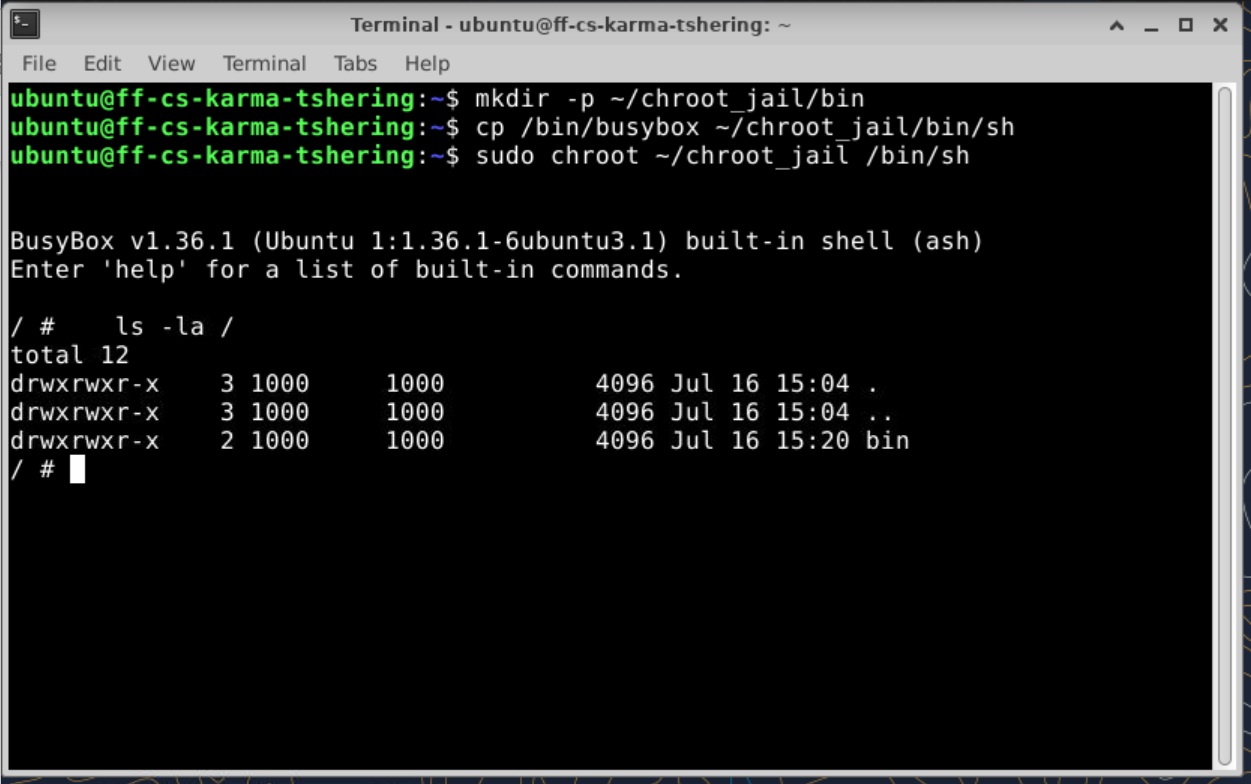
Class 5 - OS and Application security
Step 1: Create the Host Secret Flag & Set Up a Shell
sudo echo “FLAG{CHROOT_IS_NOT_A_SECURE_SANDBOX_1206}” > /host_secret.txt
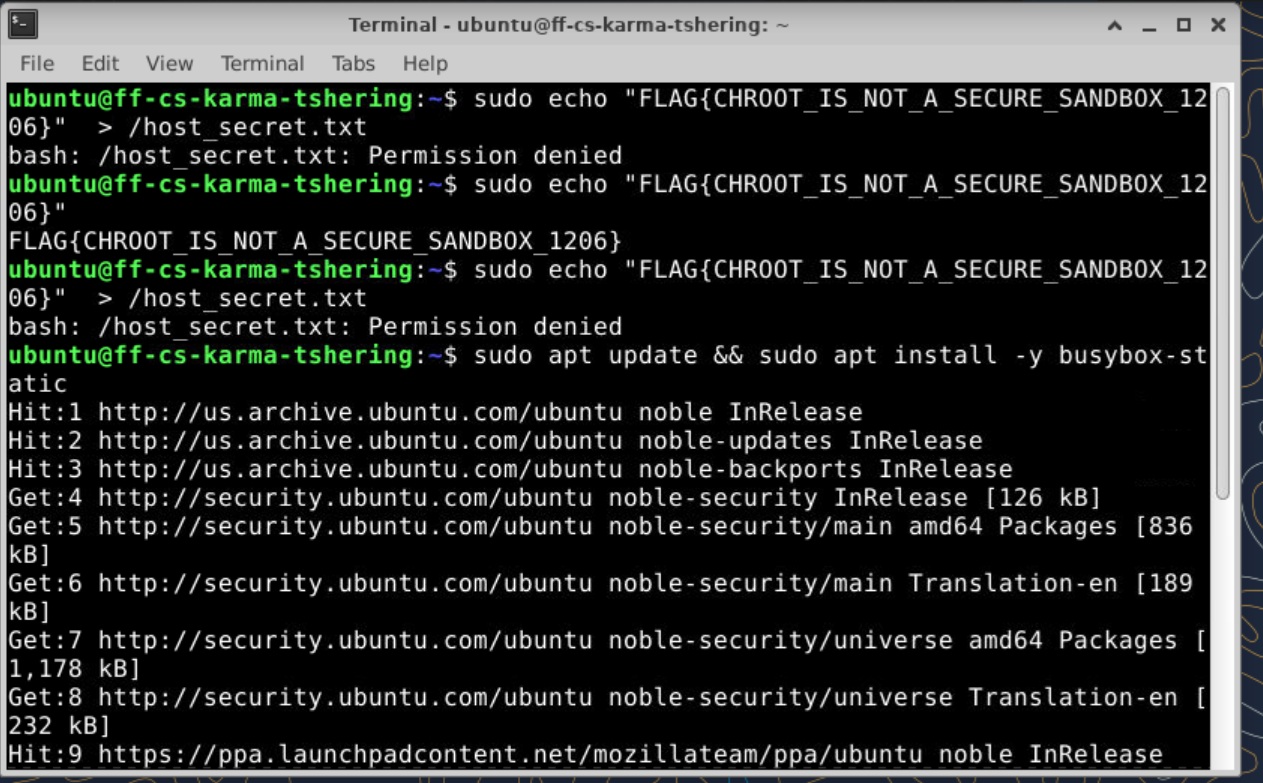
Install BusyBox and set up your sandbox environment:
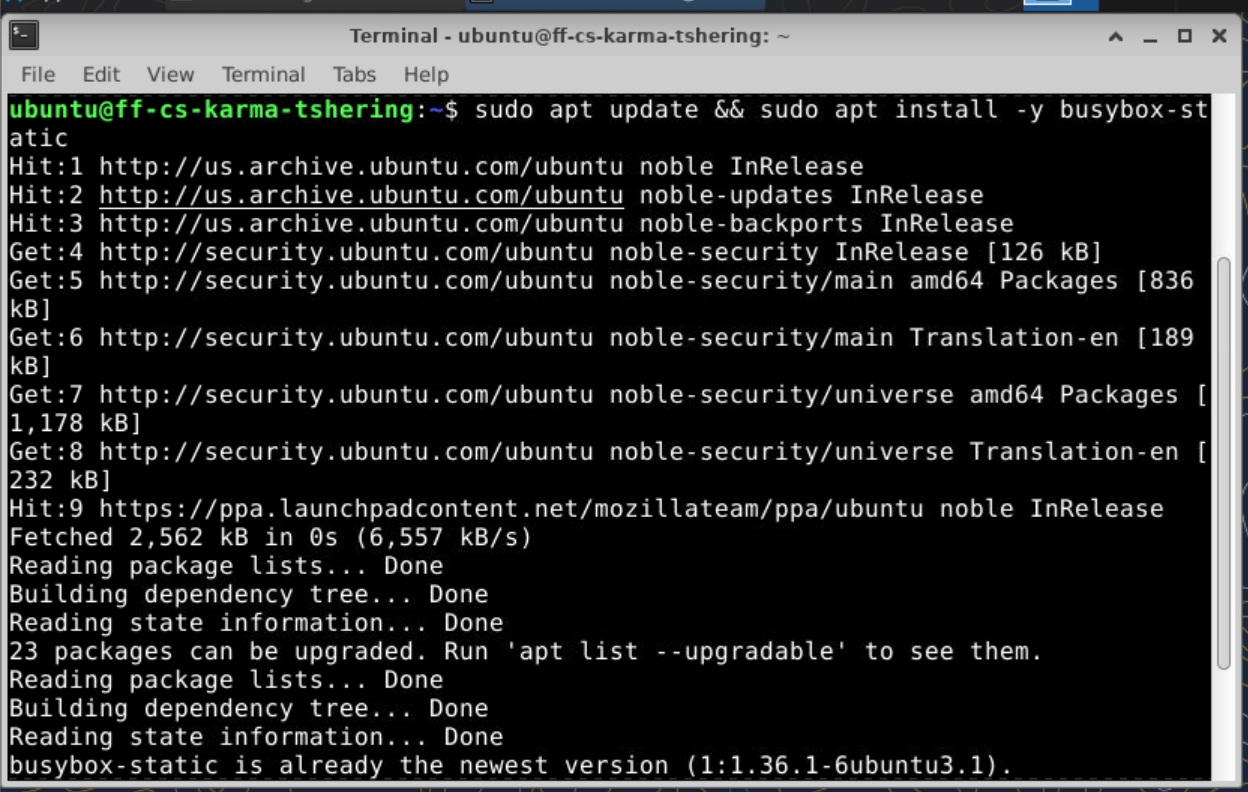
Update repositories and install the static version of BusyBox
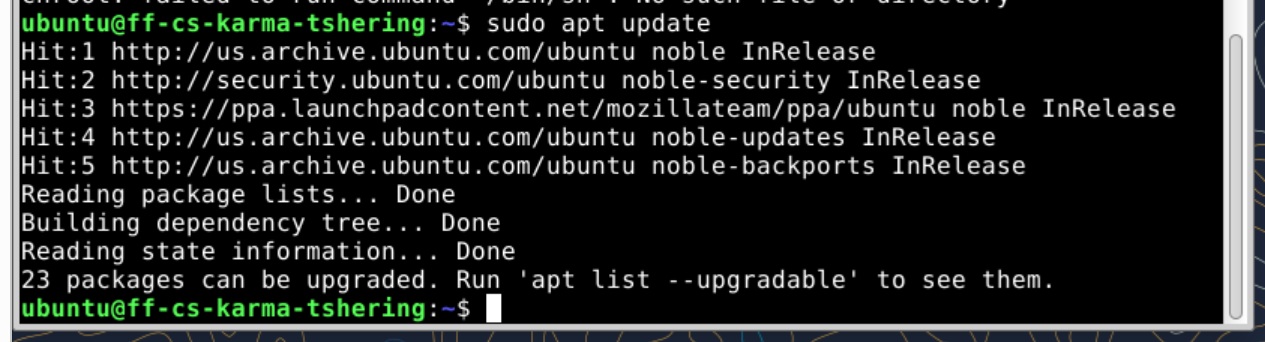
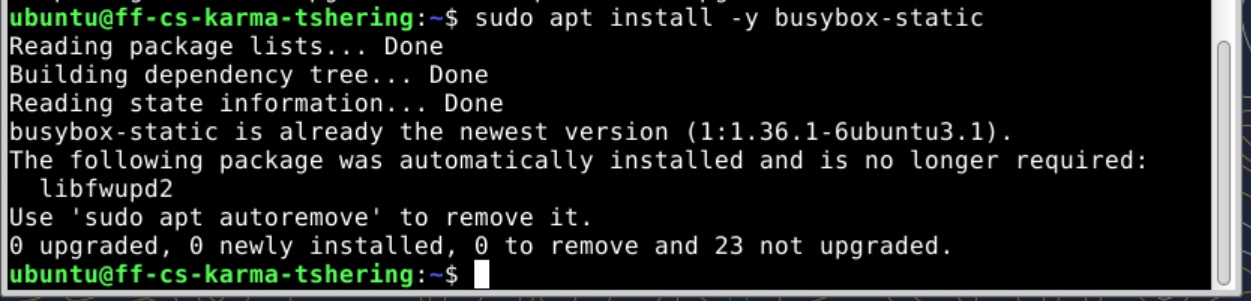
sudo apt update && sudo apt install -y busybox-static
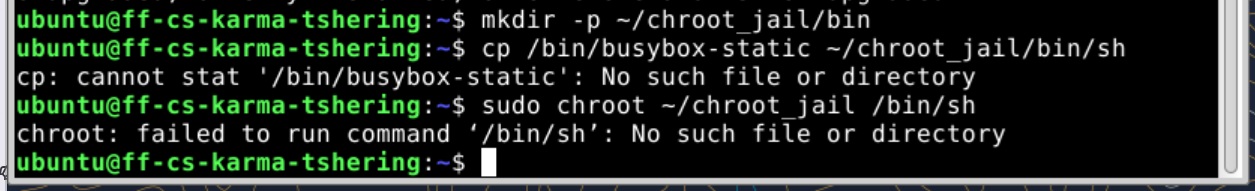
Create a clean directory structure for your jail
mkdir -p ~/chroot_jail/bin
Copy the shell we’re going to run into our “jail”
cp /bin/busybox-static ~/chroot_jail/bin/sh
Step 2: Activate the Jail!
sudo chroot ~/chroot_jail /bin/sh
Step 3: Test the Containment
List the Root Directory:
ls -la / cd ../../.. ls -la